

UUID v7, ULID & NanoID Generator
Generate cryptographically secure bulk UUID v7, UUID v4, ULID, and custom NanoID batches—or decode embedded Unix millisecond timestamps from any UUID v7 or ULID locally in your browser.
UUID v7, ULID & NanoID Generator: the tool
Identifier Settings
01950f4a-8c20-7a1b-8c3d-4e5f6a7b8c9d
01950f4a-8c21-7b2c-9d4e-5f6a7b8c9d0e
01950f4a-8c22-7c3d-ae5f-6a7b8c9d0e1f
01950f4a-8c23-7d4e-bf6a-7b8c9d0e1f2a
01950f4a-8c24-7e5f-8a7b-8c9d0e1f2a3bDesigning high-throughput databases or distributed APIs?
DEESU builds scalable PostgreSQL schemas, distributed backend services, and TypeScript APIs engineered for clean indexing and zero bottlenecks.
How it works
Why UUID v7 Replaced UUID v4 for Modern SQL Databases
For over a decade, UUID v4 was the default distributed primary key for microservices because any node could generate a globally unique 128-bit identifier without coordinating with a central sequence. However, UUID v4 has a serious performance flaw in relational databases like PostgreSQL, MySQL (InnoDB), and SQLite: its bits are completely random.
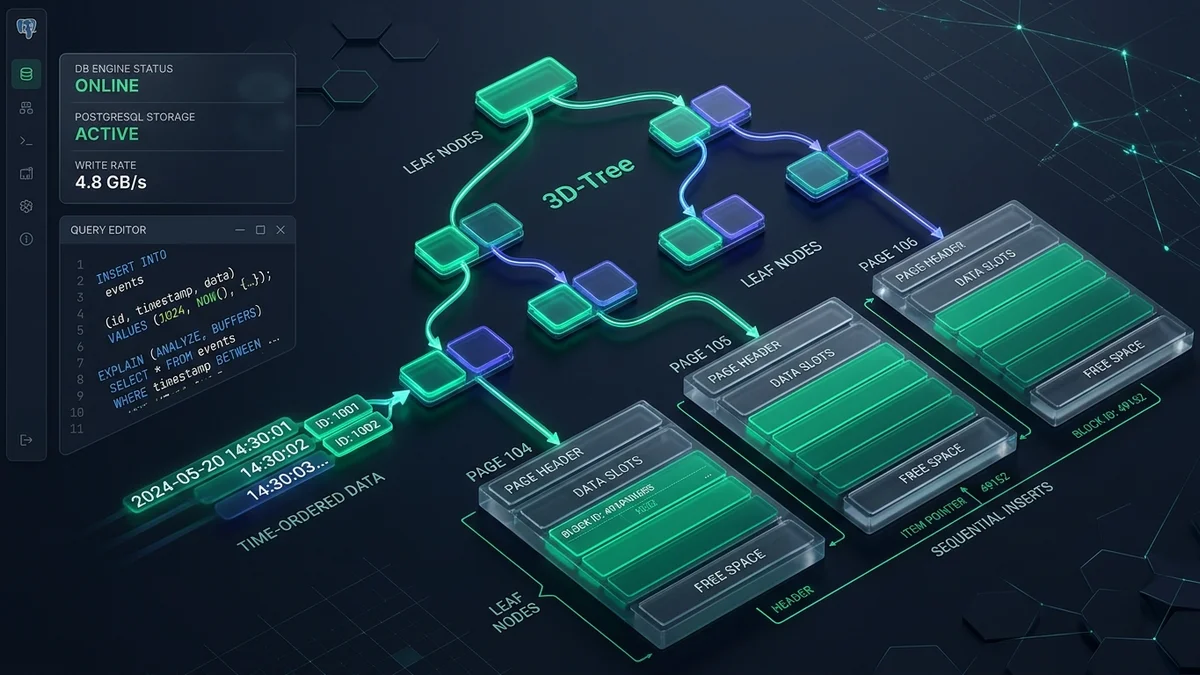
Every time a database inserts a random UUID v4 into a B-Tree primary key index, it jumps to an arbitrary page in memory or on disk. Once your index outgrows available RAM, random inserts trigger excessive page splits, high write amplification, and severe cache thrashing. RFC 9562 solved this in 2024 by standardizing UUID v7, which places a 48-bit big-endian Unix millisecond timestamp in the most significant bits followed by 74 bits of cryptographic randomness. New records always append sequentially to the rightmost edge of the B-Tree index, restoring sequential insert throughput while retaining full 128-bit UUID compatibility.
Comparing UUID v7, UUID v4, ULID, and NanoID
Choosing the right identifier format depends on your database engine, URL aesthetics, privacy requirements, and compatibility with existing tooling. Each standard makes deliberate trade-offs between sortability, string compactness, and timestamp leakage:
- UUID v7 (36 chars with hyphens, 128-bit): Best overall choice for PostgreSQL, Prisma, Drizzle, and distributed SQL primary keys. Time-ordered to the millisecond, natively stored in 16-byte
uuidcolumns, and backed by RFC 9562. - ULID (26 chars, 128-bit): Uses Crockford Base32 (no hyphens, no ambiguous I/L/O/U characters) with a 48-bit millisecond timestamp and 80 bits of randomness. Great for URLs, DynamoDB/Firestore sort keys, and human-friendly copy-paste.
- UUID v4 (36 chars, 128-bit): Contains 122 bits of pure randomness and zero timestamp information. Ideal for session tokens, password reset identifiers, or public resources where revealing creation time is undesirable.
- NanoID (default 21 chars, customizable): Uses a 64-character URL-safe alphabet (
A-Za-z0-9_-) to achieve collision resistance comparable to UUID v4 in 40% fewer characters. Perfect for short links, invite codes, and client-facing slugs.
Prefixing Public IDs (Stripe-Style Identifiers)
Many modern APIs—popularized by Stripe—prepend a short, lowercase domain prefix to every public identifier, such as usr_01950f4a..., ord_01JMC..., or tok_V1StGXR8.... Prefixing prevents costly developer mistakes where a customer ID is accidentally passed into an invoice endpoint, makes production logs immediately self-documenting, and enables automated secret scanners to detect leaked API keys.
If your database uses native 16-byte uuid columns in PostgreSQL, you can store the raw UUID v7 internally for optimal index performance and attach or strip the domain prefix at your API serialization boundary.
Cryptographic Security and Client-Side Generation
All identifiers in this tool are generated locally inside your browser using the Web Crypto API (crypto.getRandomValues), backed by your operating system's CSPRNG (cryptographically secure pseudorandom number generator). Unlike Math.random(), which uses a predictable PRNG unsuitable for security-sensitive identifiers, Web Crypto provides uniform entropy with zero network calls—your generated IDs and inspected tokens never leave your device.
Questions, answered
uuid column type with native indexing and RFC 9562 support (including native uuidv7() in PostgreSQL 18+). ULIDs are excellent when you store IDs as strings (e.g., DynamoDB, MongoDB, or URLs) and want shorter 26-character identifiers without hyphens.window.crypto.getRandomValues using unbiased bit-slicing (for ULID) and rejection sampling (for NanoID), strictly following RFC 9562 for UUID v7/v4 and the official ULID specification.usr_01950f4a-8c20-7a1b-8c3d-4e5f6a7b8c9d or ord_01JMC7X8E2K4M9P1Q2R3S4T5V6, the Inspector automatically detects and strips the prefix, validates the underlying ID, and decodes the exact UTC and local timestamp.Related reading and help
 Cloud & DevOps
UUID v7 vs UUID v4 vs ULID in 2026: Choosing the Fastest Primary Key for PostgreSQL & Distributed Systems
Compare UUID v7, UUID v4, and ULID for PostgreSQL primary keys in 2026. Fix B-Tree page splitting, cut index bloat by 40%, and benchmark insert throughput.
Nov 18, 202613 min read Web Development
PostgreSQL 17 & 18 Concurrency at Scale: BRIN, GIN, Partial Indexes & Autovacuum Tuning for 10M+ Rows
Scale PostgreSQL under heavy write concurrency. Master BRIN vs B-Tree, partial indexing, connection pooling with PgBouncer, and autovacuum tuning for 10M+ rows.
Nov 4, 20266 min read- Cloud & DevOps
ECS vs EKS: Choosing AWS Container Orchestration for a Small Engineering Team
ECS vs EKS rarely comes down to Kubernetes skill. For a small engineering team, cluster fees, ops overhead, and hiring reality decide it first.
Sep 25, 20267 min read - DEESU serviceCloud & DevOpsDeployment and CI/CD pipelines across AWS, Azure, and GCP — infrastructure that scales without a rewrite.See the service
More free tools
- Open Graph & social meta tag generatorGenerate and test Open Graph, Twitter Card, and SEO meta tags with live previews for Google, X, LinkedIn, and Facebook.
- Google Play & App Store fee calculatorCalculate your exact take-home payout, compare standard 15% vs 30% cuts, and test if external billing saves money.
- App cost calculatorEstimate a price range for an Android app or website from its features, in your local currency.
- Google Play launch checklistAn interactive checklist covering the store listing, policies, quality checks and release steps.
- Project brief generatorAnswer a few questions and get a clear, copyable brief you can send to any development team.
- App privacy policy generatorAnswer a few questions and get a plain-English privacy policy and a delete-account page for your Android or iOS app.
- App icon generatorUpload one image and download every Android, iOS and favicon size, with adaptive icon safe-zone checks.
- Play Store listing optimizerCheck your title, short and full description against keyword, readability and Google Play policy rules.
- LLM token & cost calculatorForecast production AI API expenses across OpenAI, Anthropic & DeepSeek. Model prompt caching savings and routing arbitrage.
- JWT debugger & security inspectorDecode, verify, and audit JSON Web Tokens for alg:none bypasses, key confusion attacks, expiry status and leaked secrets.
- Cron expression generator & explainerBuild, validate and translate crontab schedules for Linux, AWS EventBridge, GitHub Actions and Kubernetes.
- JSON to TypeScript & Zod converterInstantly convert raw API JSON payloads into clean TypeScript interfaces and production Zod v3 validation schemas.
- Docker Run to Docker Compose converterConvert raw docker run commands into production Docker Compose v2 YAML with automated security hardening and healthchecks.
- cURL to Code converter (Fetch, Axios, Python, Go)Translate cURL commands into JavaScript fetch, Axios, Python requests, Go, Rust, and Node.js with 100% in-browser privacy.
- SVG optimizer & React JSX converterMinify and clean vector SVGs, strip Figma metadata, and convert to production React JSX, React Native, or Vue components.
- Regex tester, debugger & ReDoS auditorTest regular expressions live with capture groups, replace previews, plain-English explanations, and catastrophic backtracking detection.
- JSON formatter, validator & diff viewerBeautify, validate, minify, sort keys, and compare two JSON payloads side by side with nested JSONPath diff inspection.
- SQL formatter & query linterBeautify PostgreSQL, MySQL, SQLite, and T-SQL queries and catch SELECT *, missing WHERE clauses, and slow non-sargable scans.
- CSS to Tailwind v4 converter & OKLCH paletteConvert raw CSS declarations to Tailwind v4 utility classes and generate accessible 50–950 OKLCH color scales with @theme export.
- Base64, URL, HTML & SHA-256 hash toolkitEncode/decode Base64 (UTF-8 & URL-safe), URLs, HTML entities, Hex, and generate SHA-256, SHA-512 & HMAC signatures offline.
- Linux chmod permissions calculatorCalculate Linux octal and symbolic file permissions (755, 644, 600), configure SetUID/SetGID/Sticky bits, and export chmod commands.
- Robots.txt generator & AI bot blockerBuild valid robots.txt rules, control GPTBot, ClaudeBot, and CCBot AI crawlers, declare sitemaps, and test URL paths live.
- CSP & HTTP security headers generatorGenerate strict Content-Security-Policy, HSTS, and Permissions-Policy configs for Next.js, Vercel, Nginx, Apache, and Cloudflare.
- Markdown table & GitHub README builderCreate formatted Markdown tables visually, import CSV/TSV spreadsheets, and build GitHub alert callouts and Shields.io badges.
Tell us what you're building.
Send the problem, not a polished brief. We'll tell you what it actually takes to ship it: stack, timeline and cost, before you commit to anything.