

SQL Formatter & Query Linter
Beautify PostgreSQL, MySQL, SQLite, and T-SQL queries with clean clause alignment while automatically catching SELECT *, missing WHERE mutations, and index-breaking anti-patterns.
SQL Formatter & Query Linter: the tool
SELECT
  o.id,
  c.email,
  c.country_code,
  count(oi.id) AS line_items,
  sum(oi.quantity * oi.unit_price) AS gross_revenue
FROM orders o
INNER JOIN customers c
  ON c.id = o.customer_id
LEFT JOIN order_items oi
  ON oi.order_id = o.id
WHERE o.status = 'paid'
  AND o.created_at >= '2026-01-01'
GROUP BY o.id, c.email, c.country_code
HAVING sum(oi.quantity * oi.unit_price) > 250
ORDER BY gross_revenue DESC
LIMIT 100;
SQL Performance & Safety Linter
Static audit for PostgreSQL safety rules, indexability, and pagination patterns
Clean Query — No Static Anti-Patterns Detected
This query uses explicit projections, bounded execution, and passes static indexability checks. Always verify production execution plans with EXPLAIN ANALYZE.
Battling slow PostgreSQL queries, lock contention, or growing cloud DB bills?
DEESU performs deep EXPLAIN ANALYZE audits, composite indexing, query rewrites, and zero-downtime schema migrations.
How it works
Why Clean SQL Formatting Directly Improves Query Reliability
SQL is uniquely vulnerable to silent logic bugs when compressed into single-line strings inside ORM logs, migration files, or BI dashboards. Misplaced AND/OR precedence, accidental Cartesian joins, and missing WHERE clauses hide easily inside unformatted queries.
Our tokenizer-based SQL formatter parses string literals, line comments (--), block comments (/* ... */), operators, and parenthesized subqueries without corrupting quoted data. It aligns every major clause (SELECT, FROM, JOIN, WHERE, GROUP BY, HAVING, ORDER BY, LIMIT) consistently so code reviews take seconds instead of minutes.
Understanding Sargable Queries and B-Tree Index Performance
A query predicate is called SARGable (Search ARGument-able) when the database query planner can use an index seek instead of reading every row in the table. Two of the most frequent production performance killers in PostgreSQL, MySQL, and SQL Server break sargability instantly:
- Leading Wildcard LIKE (
LIKE '%@gmail.com'): Because B-Tree indexes sort strings from left to right, a leading%forces a full sequential scan across millions of rows. - Functions Wrapping Indexed Columns (
LOWER(email) = ...orYEAR(created_at) = 2026): The planner cannot compare raw index entries against a transformed expression unless you create a dedicated expression index or rewrite dates as half-open ranges (created_at >= '2026-01-01' AND created_at < '2027-01-01'). - Deep OFFSET Pagination (
OFFSET 25000): The database still fetches and sorts 25,050 rows before discarding the first 25,000. Switching to keyset pagination keeps page latency flat in O(log n) time.
Preventing Production Outages With Static SQL Safety Checks
Beyond slow reads, unguarded write statements cause the highest-severity incidents in database operations. Running an UPDATE or DELETE without a WHERE clause modifies every row in the table instantaneously. Similarly, NOT IN (SELECT ...) contains a classic SQL three-valued logic trap: if the subquery returns a single NULL, the entire NOT IN expression evaluates to UNKNOWN, silently returning zero rows.
Running every ad-hoc migration, hotfix, or analytical query through a static linter before executing it against staging or production catches these anti-patterns before they touch live customer data.
Dialect Portability Across PostgreSQL, MySQL, SQLite, and T-SQL
While ANSI SQL shares core syntax across engines, dialect differences frequently trip up full-stack developers switching between projects. PostgreSQL uses double quotes for case-sensitive identifiers and ILIKE / pg_trgm for case-insensitive matching; MySQL uses backticks; and Microsoft SQL Server (T-SQL) uses TOP or OFFSET ... FETCH NEXT instead of LIMIT. Selecting your target dialect tailors the linter's optimization recommendations to the exact engine you run in production.
Questions, answered
SELECT * prevents index-only covering scans, wastes network serialization on unused JSONB/TEXT columns, and can break downstream application deserializers whenever columns are added or reordered in migrations.x != NULL evaluates to UNKNOWN, if a subquery inside NOT IN returns even one NULL value, the entire WHERE condition fails for every row. Rewriting it as NOT EXISTS avoids the NULL trap completely.WHERE (created_at, id) < ($1, $2) ORDER BY created_at DESC, id DESC LIMIT 50) backed by a composite index on (created_at DESC, id DESC).-- line comments, and /* ... */ block comments separately so keyword casing and indentation never modify data inside strings.Related reading and help
 Cloud & DevOps
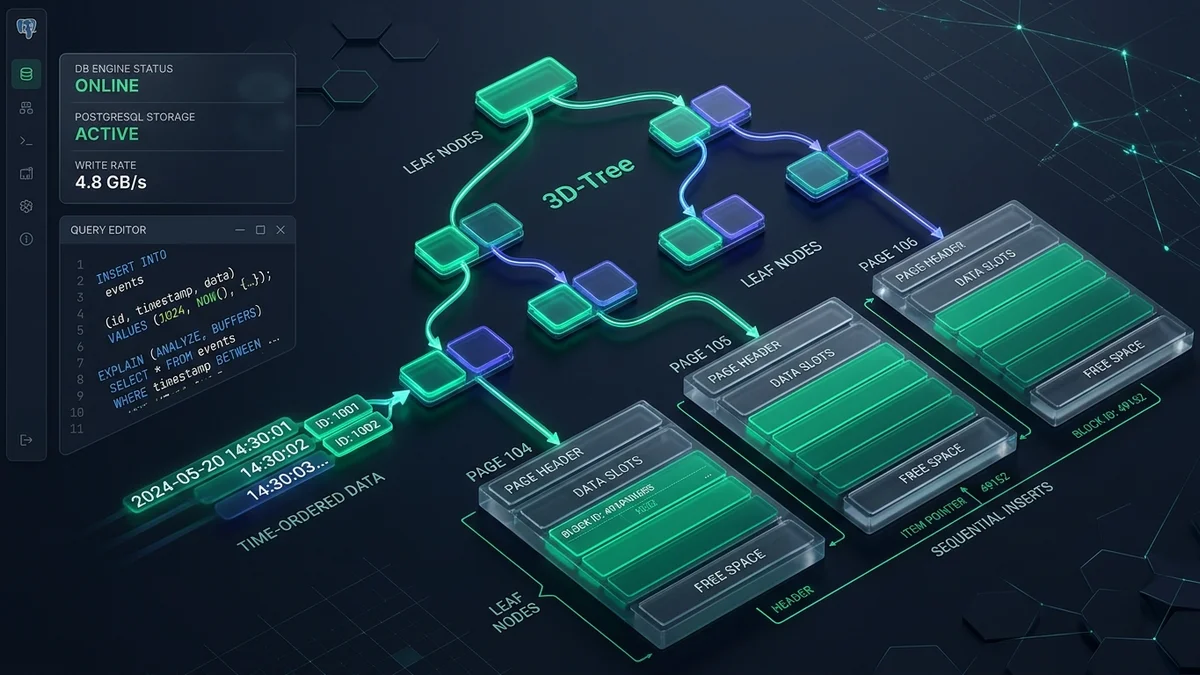
UUID v7 vs UUID v4 vs ULID in 2026: Choosing the Fastest Primary Key for PostgreSQL & Distributed Systems
Compare UUID v7, UUID v4, and ULID for PostgreSQL primary keys in 2026. Fix B-Tree page splitting, cut index bloat by 40%, and benchmark insert throughput.
Nov 18, 202613 min read Web Development
PostgreSQL 17 & 18 Concurrency at Scale: BRIN, GIN, Partial Indexes & Autovacuum Tuning for 10M+ Rows
Scale PostgreSQL under heavy write concurrency. Master BRIN vs B-Tree, partial indexing, connection pooling with PgBouncer, and autovacuum tuning for 10M+ rows.
Nov 4, 20266 min read Web Development
PostgreSQL pgvector in Production: HNSW Indexes, Hybrid Semantic Search & RAG Without Dedicated Vector DBs
Deploy pgvector in production PostgreSQL in 2026. Master HNSW indexing, quantization, hybrid BM25 full-text search, and Reciprocal Rank Fusion RAG pipelines.
Nov 6, 20266 min read- DEESU serviceCloud & DevOpsDeployment and CI/CD pipelines across AWS, Azure, and GCP — infrastructure that scales without a rewrite.See the service
More free tools
- Open Graph & social meta tag generatorGenerate and test Open Graph, Twitter Card, and SEO meta tags with live previews for Google, X, LinkedIn, and Facebook.
- Google Play & App Store fee calculatorCalculate your exact take-home payout, compare standard 15% vs 30% cuts, and test if external billing saves money.
- App cost calculatorEstimate a price range for an Android app or website from its features, in your local currency.
- Google Play launch checklistAn interactive checklist covering the store listing, policies, quality checks and release steps.
- Project brief generatorAnswer a few questions and get a clear, copyable brief you can send to any development team.
- App privacy policy generatorAnswer a few questions and get a plain-English privacy policy and a delete-account page for your Android or iOS app.
- App icon generatorUpload one image and download every Android, iOS and favicon size, with adaptive icon safe-zone checks.
- Play Store listing optimizerCheck your title, short and full description against keyword, readability and Google Play policy rules.
- LLM token & cost calculatorForecast production AI API expenses across OpenAI, Anthropic & DeepSeek. Model prompt caching savings and routing arbitrage.
- JWT debugger & security inspectorDecode, verify, and audit JSON Web Tokens for alg:none bypasses, key confusion attacks, expiry status and leaked secrets.
- Cron expression generator & explainerBuild, validate and translate crontab schedules for Linux, AWS EventBridge, GitHub Actions and Kubernetes.
- JSON to TypeScript & Zod converterInstantly convert raw API JSON payloads into clean TypeScript interfaces and production Zod v3 validation schemas.
- Docker Run to Docker Compose converterConvert raw docker run commands into production Docker Compose v2 YAML with automated security hardening and healthchecks.
- cURL to Code converter (Fetch, Axios, Python, Go)Translate cURL commands into JavaScript fetch, Axios, Python requests, Go, Rust, and Node.js with 100% in-browser privacy.
- SVG optimizer & React JSX converterMinify and clean vector SVGs, strip Figma metadata, and convert to production React JSX, React Native, or Vue components.
- Regex tester, debugger & ReDoS auditorTest regular expressions live with capture groups, replace previews, plain-English explanations, and catastrophic backtracking detection.
- JSON formatter, validator & diff viewerBeautify, validate, minify, sort keys, and compare two JSON payloads side by side with nested JSONPath diff inspection.
- CSS to Tailwind v4 converter & OKLCH paletteConvert raw CSS declarations to Tailwind v4 utility classes and generate accessible 50–950 OKLCH color scales with @theme export.
- Base64, URL, HTML & SHA-256 hash toolkitEncode/decode Base64 (UTF-8 & URL-safe), URLs, HTML entities, Hex, and generate SHA-256, SHA-512 & HMAC signatures offline.
- UUID v7, UUID v4, ULID & NanoID generatorBulk generate cryptographically secure RFC 9562 UUID v7, UUID v4, ULID, and custom NanoIDs and decode embedded timestamps.
- Linux chmod permissions calculatorCalculate Linux octal and symbolic file permissions (755, 644, 600), configure SetUID/SetGID/Sticky bits, and export chmod commands.
- Robots.txt generator & AI bot blockerBuild valid robots.txt rules, control GPTBot, ClaudeBot, and CCBot AI crawlers, declare sitemaps, and test URL paths live.
- CSP & HTTP security headers generatorGenerate strict Content-Security-Policy, HSTS, and Permissions-Policy configs for Next.js, Vercel, Nginx, Apache, and Cloudflare.
- Markdown table & GitHub README builderCreate formatted Markdown tables visually, import CSV/TSV spreadsheets, and build GitHub alert callouts and Shields.io badges.
Tell us what you're building.
Send the problem, not a polished brief. We'll tell you what it actually takes to ship it: stack, timeline and cost, before you commit to anything.